
WASHINGTON – Five federal agencies are warning grocery retailers and other cold-storage operators to strengthen cybersecurity protections as hackers increasingly target commercial refrigeration and temperature-monitoring systems worldwide.
In a joint advisory issued on November 5, the Cybersecurity and Infrastructure Security Agency (CISA), the FBI, and the departments of Health and Human Services, Agriculture, and Transportation said that malicious actors are exploiting vulnerabilities in internet-connected refrigeration controllers to manipulate temperatures, disrupt operations, and potentially destroy perishable inventory.
The warning comes after a series of cyberattacks in Europe, including an October incident that disrupted refrigeration systems at about 700 supermarkets across France. French authorities have since accused Iran’s Islamic Revolutionary Guard Corps of orchestrating those attacks, which caused extensive food spoilage, equipment damage and about 20 fires.
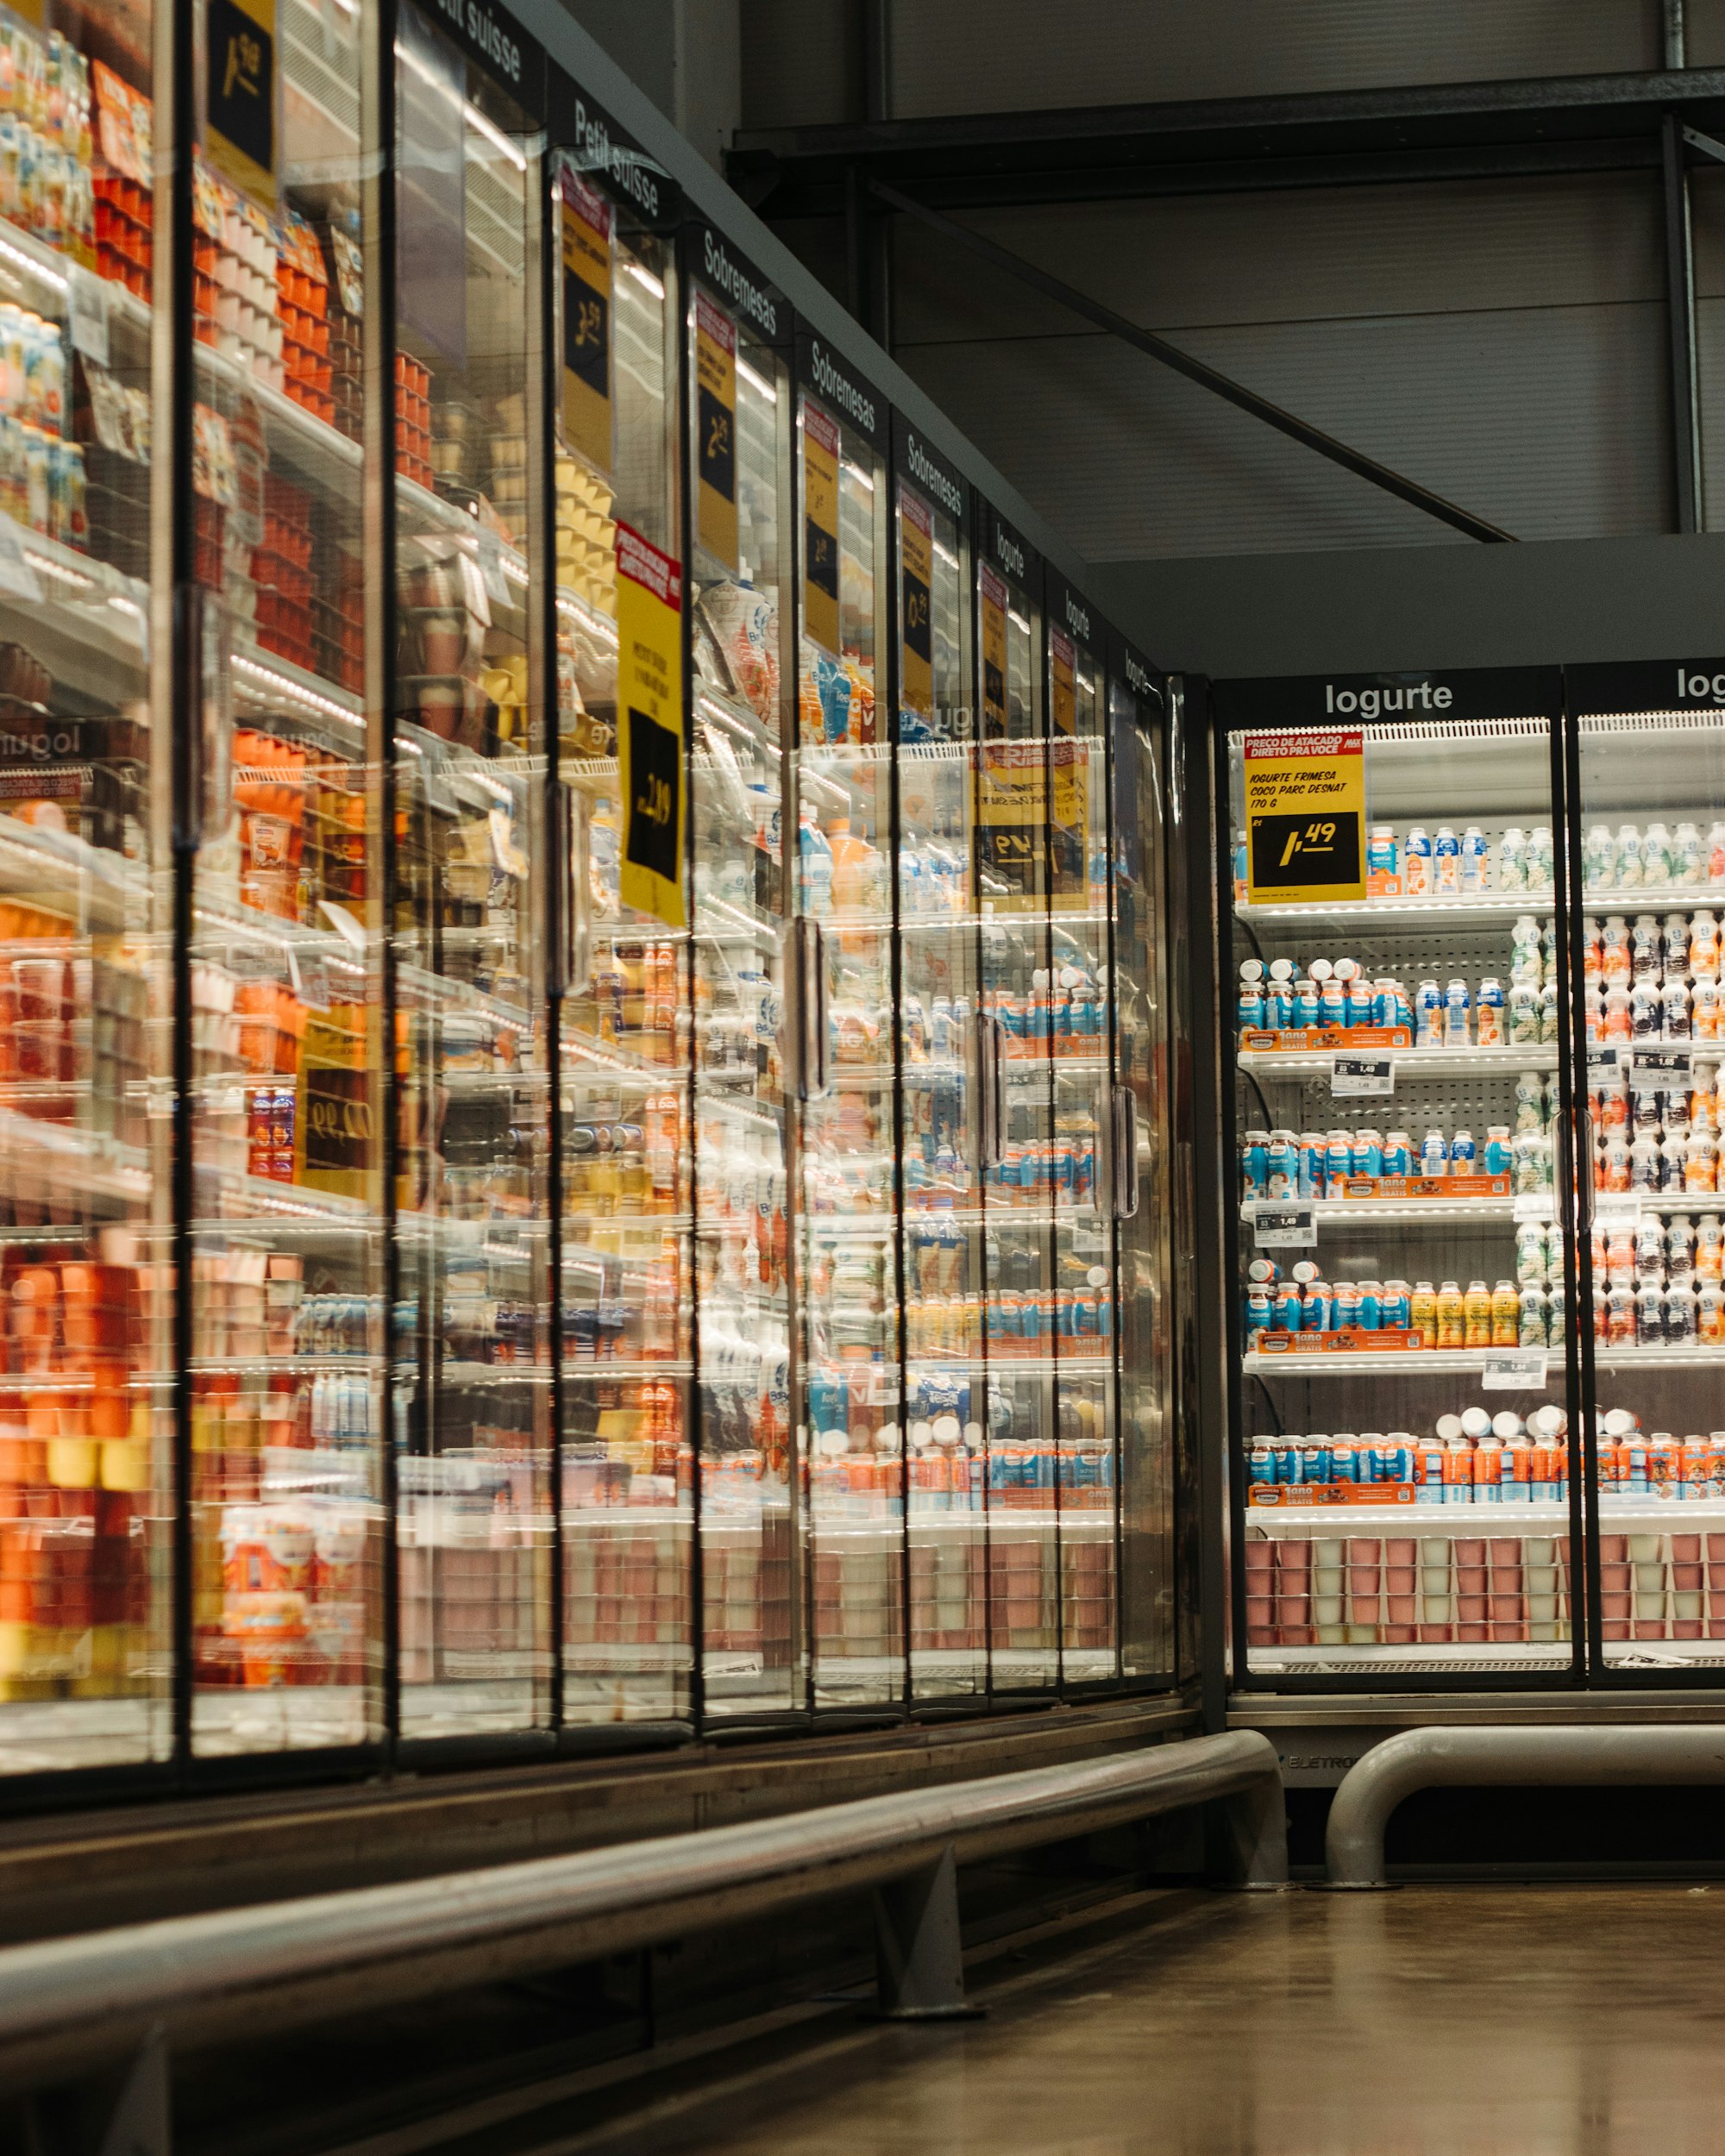
According to the federal advisory, attackers are targeting electronic temperature controllers and commercial refrigeration systems in grocery stores, cold-storage facilities and refrigerated transportation.
Hackers may exploit outdated software, weak security configurations, or authentication vulnerabilities to gain remote access to equipment. Once inside, they can alter temperature settings, force refrigeration units into continuous heating or defrost cycles, and interfere with systems that monitor storage conditions.
Such intrusions can cause widespread inventory losses, shorten equipment life, and create fire hazards. The agencies also warned that compromised temperature-monitoring systems could prevent operators from identifying unsafe storage conditions, potentially exposing consumers to improperly stored food.
“Every organization that depends on refrigeration and monitoring systems should assume it could be a target,” said Chris Butera, CISA’s acting executive assistant director for cybersecurity, in comments reported by Reuters.
Federal officials urged retailers and other operators to immediately review their systems and eliminate unnecessary public internet access to refrigeration controllers. When remote access is required, businesses should secure connections using updated firewalls and other protective measures.
The advisory also recommends separating operational technology from corporate networks, replacing default passwords, implementing multifactor authentication where feasible, and keeping device firmware updated.
Operators are also encouraged to retire unsupported equipment, maintain offline backups, monitor for suspicious activity, and establish temperature limits to prevent systems from operating outside safe ranges.
The warning comes amid ongoing investigations into refrigeration-related cyber incidents across Europe and the United States.
 Thorvardur de Shong
As MMR previously reported, French authorities say hackers manipulated refrigeration controls at major grocery chains, including Intermarché, Netto, Coopérative U, Carrefour, Monoprix, and E.Leclerc. A second wave of attacks in early November affected more than 100 establishments across several European countries.
Pentagon investigators are also examining suspected cyberattacks on refrigeration equipment at U.S. military commissaries in August. Authorities have not established a link between those incidents and the European attacks.
The U.S. advisory did not identify a specific country or a hacking group responsible for the global activity.
 Thorvardur de Shong
For grocery retailers, the federal warning underscores the need to safeguard connected refrigeration equipment as part of broader cybersecurity and business continuity planning. Unlike conventional data breaches, attacks on operational technology can directly threaten food safety, destroy inventory, and disrupt store operations.
Submit Your Press Release
Have news to share? Send us your press releases and announcements.
Send Press Release


